

Xray
Learn what JFrog Xray is and where it fits across your software lifecycle.
JFrog Xray is a Software Composition Analysis (SCA) tool that scans source code and binaries to detect vulnerabilities, malicious packages, license risks, and operational issues across supported technologies and LLM model scanning. Powered by JFrog Security Research, Xray provides advanced threat information based on the group's enriched CVE information.
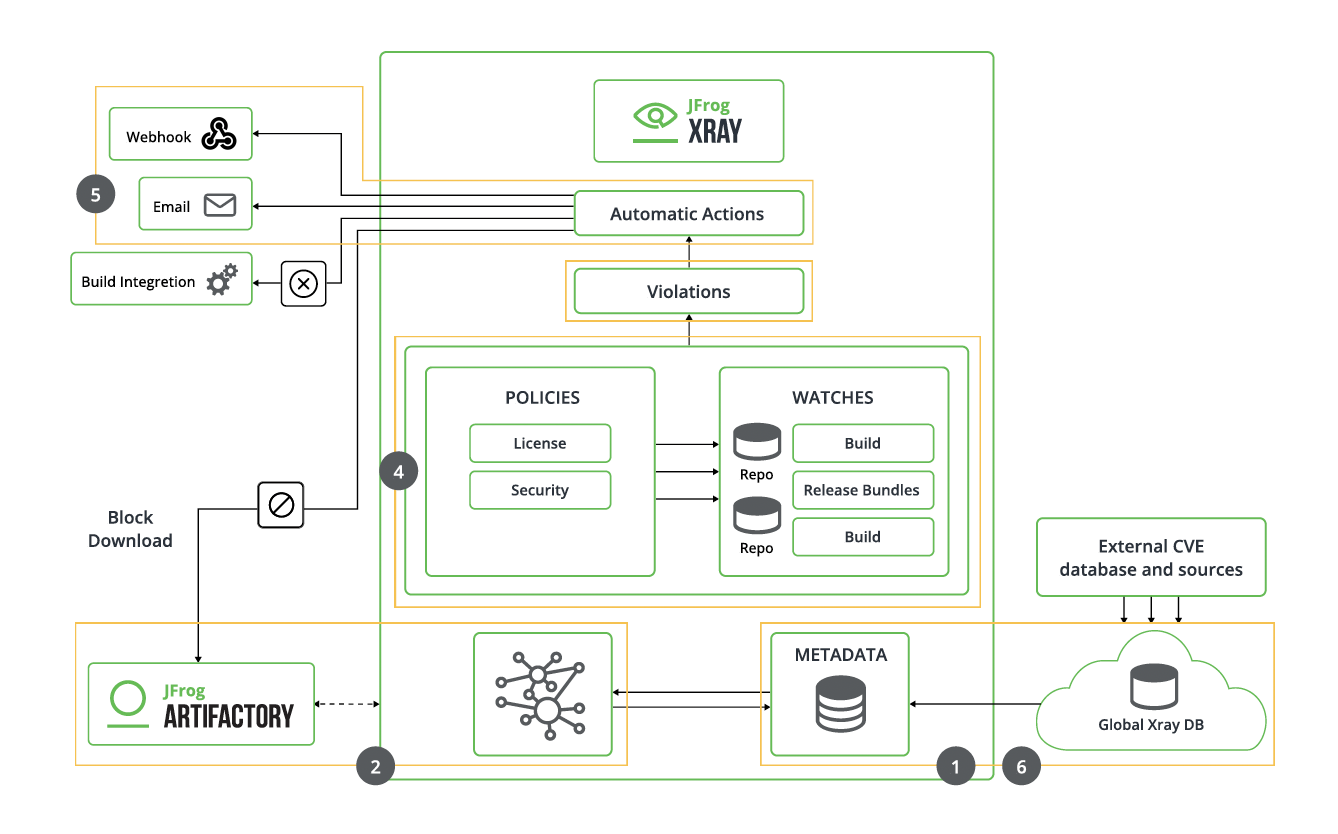
Xray integrates natively with JFrog Artifactory, enabling binary scanning with a single checkbox. For source code, Frogbot and IDE plugins provide immediate feedback and autofixes, while build-info scanning analyzes builds to catch risks introduced during the build process.
Xray’s policies and watches help enforce security and compliance thresholds by flagging risky components. With Impact Analysis, it continuously monitors emerging threats and alerts teams to new vulnerabilities in existing components.
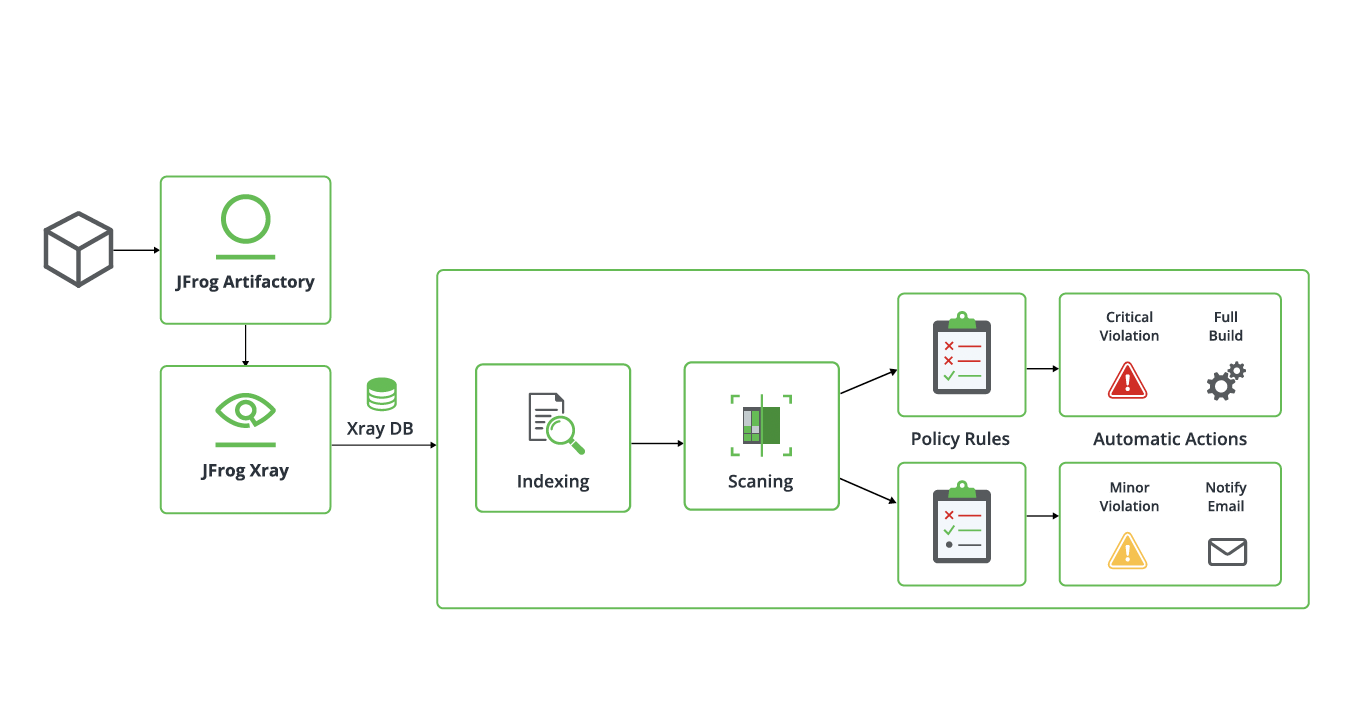
Comprehensive Security Coverage
Combining source code and binary scanning, Xray delivers shift-left security for early detection and binary-level validation for final artifact safety. This ensures end-to-end protection across the entire software development lifecycle. For more information, see Scan Types.
Where Xray Fits in the JFrog Security Timeline
Security in the software development process must be continuous, spanning from code development to deployment and beyond. JFrog Xray integrates into multiple stages of the software lifecycle, ensuring that security is proactive rather than reactive.
The following table shows where Xray fits at each stage of the JFrog security timeline.
| Stage | Xray's Role |
|---|---|
| Code Development (Developers) | Scans dependencies in IDEs & CLI before committing code. |
| Code Merge (SCM) | Scans dependencies using Frogbot to make sure Pull requests do not introduce new security issues. It can also create Pull requests to auto-fix risky dependencies. |
| Build & Package (CI/CD Security) | Scans builds in CI/CD pipelines to detect vulnerabilities. |
| Artifact Management (Repository Security) | Continuously scans Artifactory repositories for security, compliance, and operational risks. |
| Release Validation (Pre-Deployment Security) | Scans release bundles before promotion or distribution to ensure compliance and security. |
| Production & Runtime Security (Requires JFrog Runtime) | Monitors for newly discovered vulnerabilities in already deployed artifacts. |
Xray Installation
For more information, see Installing Xray.
Business Needs for JFrog Xray
Securing your software supply chain brings increasing challenges. Key concerns include:
- Managing Software Bill of Materials (SBOM)
Xray supports ingesting and exporting SBOMs, including CycloneDX, to provide visibility into your software components. This ensures transparency and helps track dependencies across the software supply chain. - Policy Enforcement and Integrations
Xray enforces security policies through integrations with systems like Jira and webhooks. Automated alerts and effective alerting workflows ensure teams are quickly informed about vulnerabilities, keeping security issues in check across the development lifecycle. - Detecting Malicious Components
Xray scans dependencies for known vulnerabilities and malicious packages, alerting teams to compromised components before they can affect the development process or enter production, helping reduce the risk of supply chain attacks. - Reducing Security Overhead
Xray automates vulnerability detection and policy enforcement, while Frogbot offers autofix capabilities. This reduces manual effort, allowing security teams to focus on critical tasks while ensuring continuous security monitoring. - Improving Development Efficiency
Xray helps developers catch vulnerable or non-compliant dependencies early using Frogbot and IDE plugins. This reduces rework, speeds up development, and maintains security throughout the process.
Frequently Asked Questions
This section provides answers to frequently asked questions.
FAQs
Q: What is JFrog Xray?
A: JFrog Xray is an SCA tool that scans source code and binaries for vulnerabilities, malicious packages, license risks, and operational issues. It is powered by JFrog Security Research and integrates with Artifactory, Frogbot, and IDE plugins.
Q: What is the difference between source code scanning and binary scanning in Xray?
A: Source code scanning gives early feedback in IDEs, CLI, and pull requests, while binary scanning validates packaged artifacts in Artifactory. Together they provide shift-left detection and final artifact safety. For more information, see Comprehensive Security Coverage.
Q: Where does Xray fit in the software development lifecycle?
A: Xray covers stages from code development through merge, CI/CD, Artifactory repositories, release validation, and production monitoring with JFrog Runtime. For more information, see Where Xray Fits in the JFrog Security Timeline.
Q: Can Xray help manage Software Bills of Materials (SBOMs)?
A: Yes. Xray supports ingesting and exporting SBOMs, including CycloneDX, so you can track components and dependencies across your software supply chain. For more information, see Business Needs for JFrog Xray and SBOM.
Q: How do policies and watches help with Xray?
A: Policies define security and compliance thresholds, and watches apply them to resources so Xray can flag risky components and trigger alerts or other actions. For more information, see Policies in JFrog Xray and Watches in JFrog Xray.
Related Topics
Updated 27 days ago